GovernX
Continuous Governance and Risk Monitoring
GovernX is an AI-powered continuous governance and compliance platform that turns policies, regulations and controls into continuously monitored, actionable intelligence.
It helps organizations identify risks, control gaps and compliance issues before they become audit findings, moving governance from periodic audits to continuous assurance.
Bring policies, controls and transactions together for continuous risk monitoring.
From periodic, sample-based audits
Periodic audits cover only part of what happened, creating a gap between when risk occurs and when it is found.
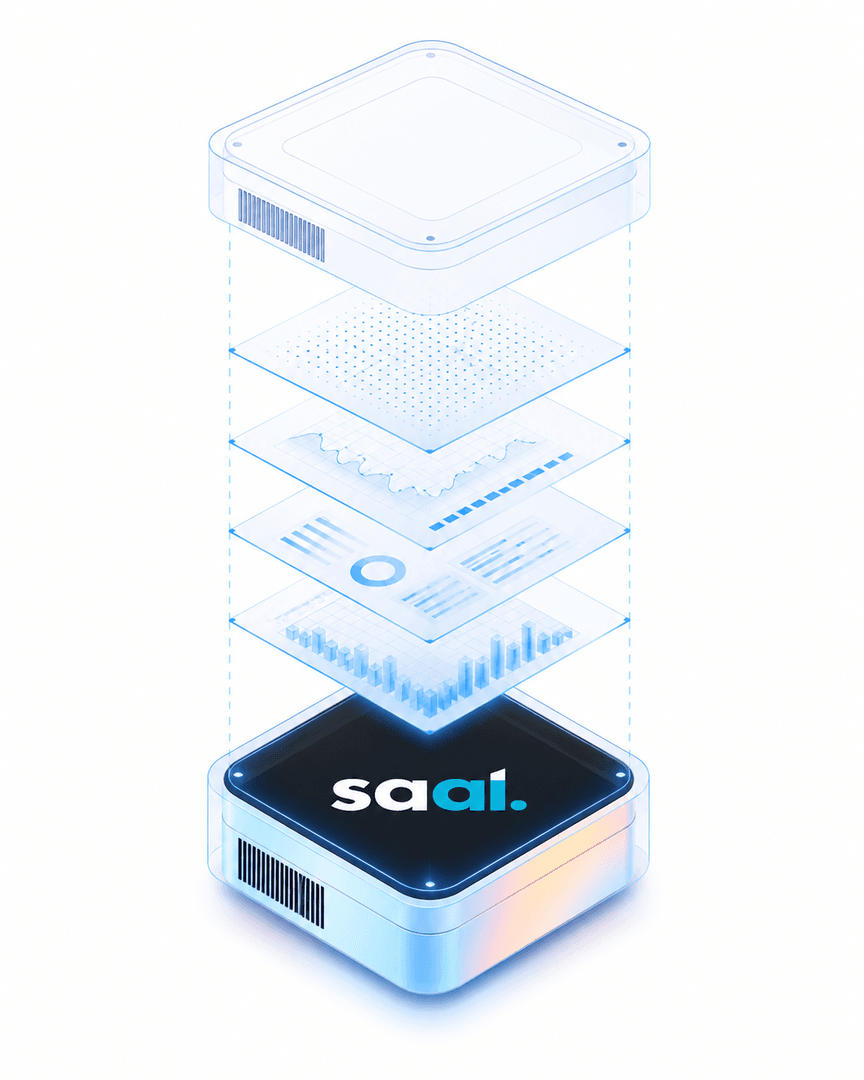
to always-on assurance
GovernX creates a live, connected view of organizational activity and surfaces policy breaches, anomalies and control failures with traceable evidence.
A Closer Look at the Product
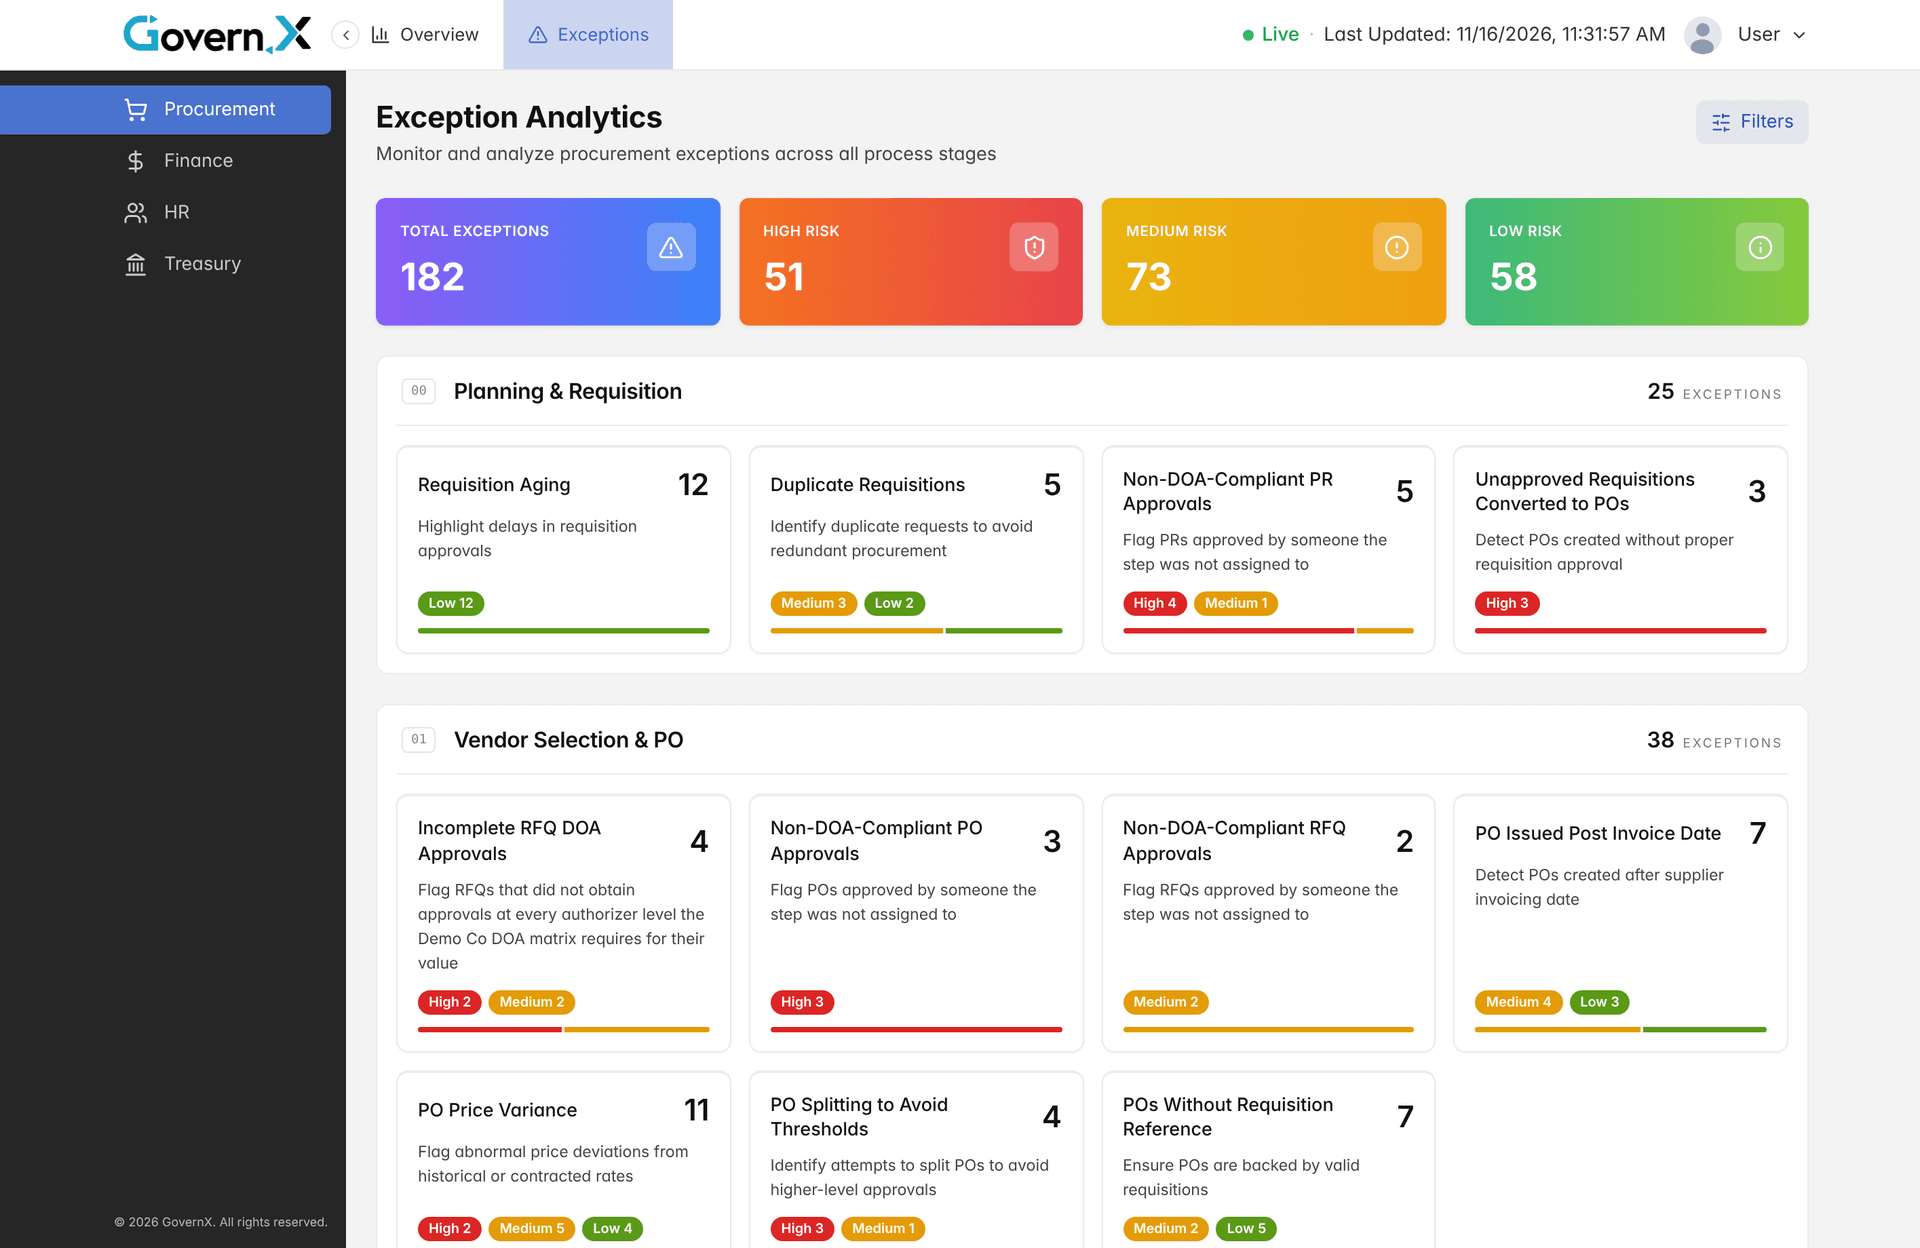
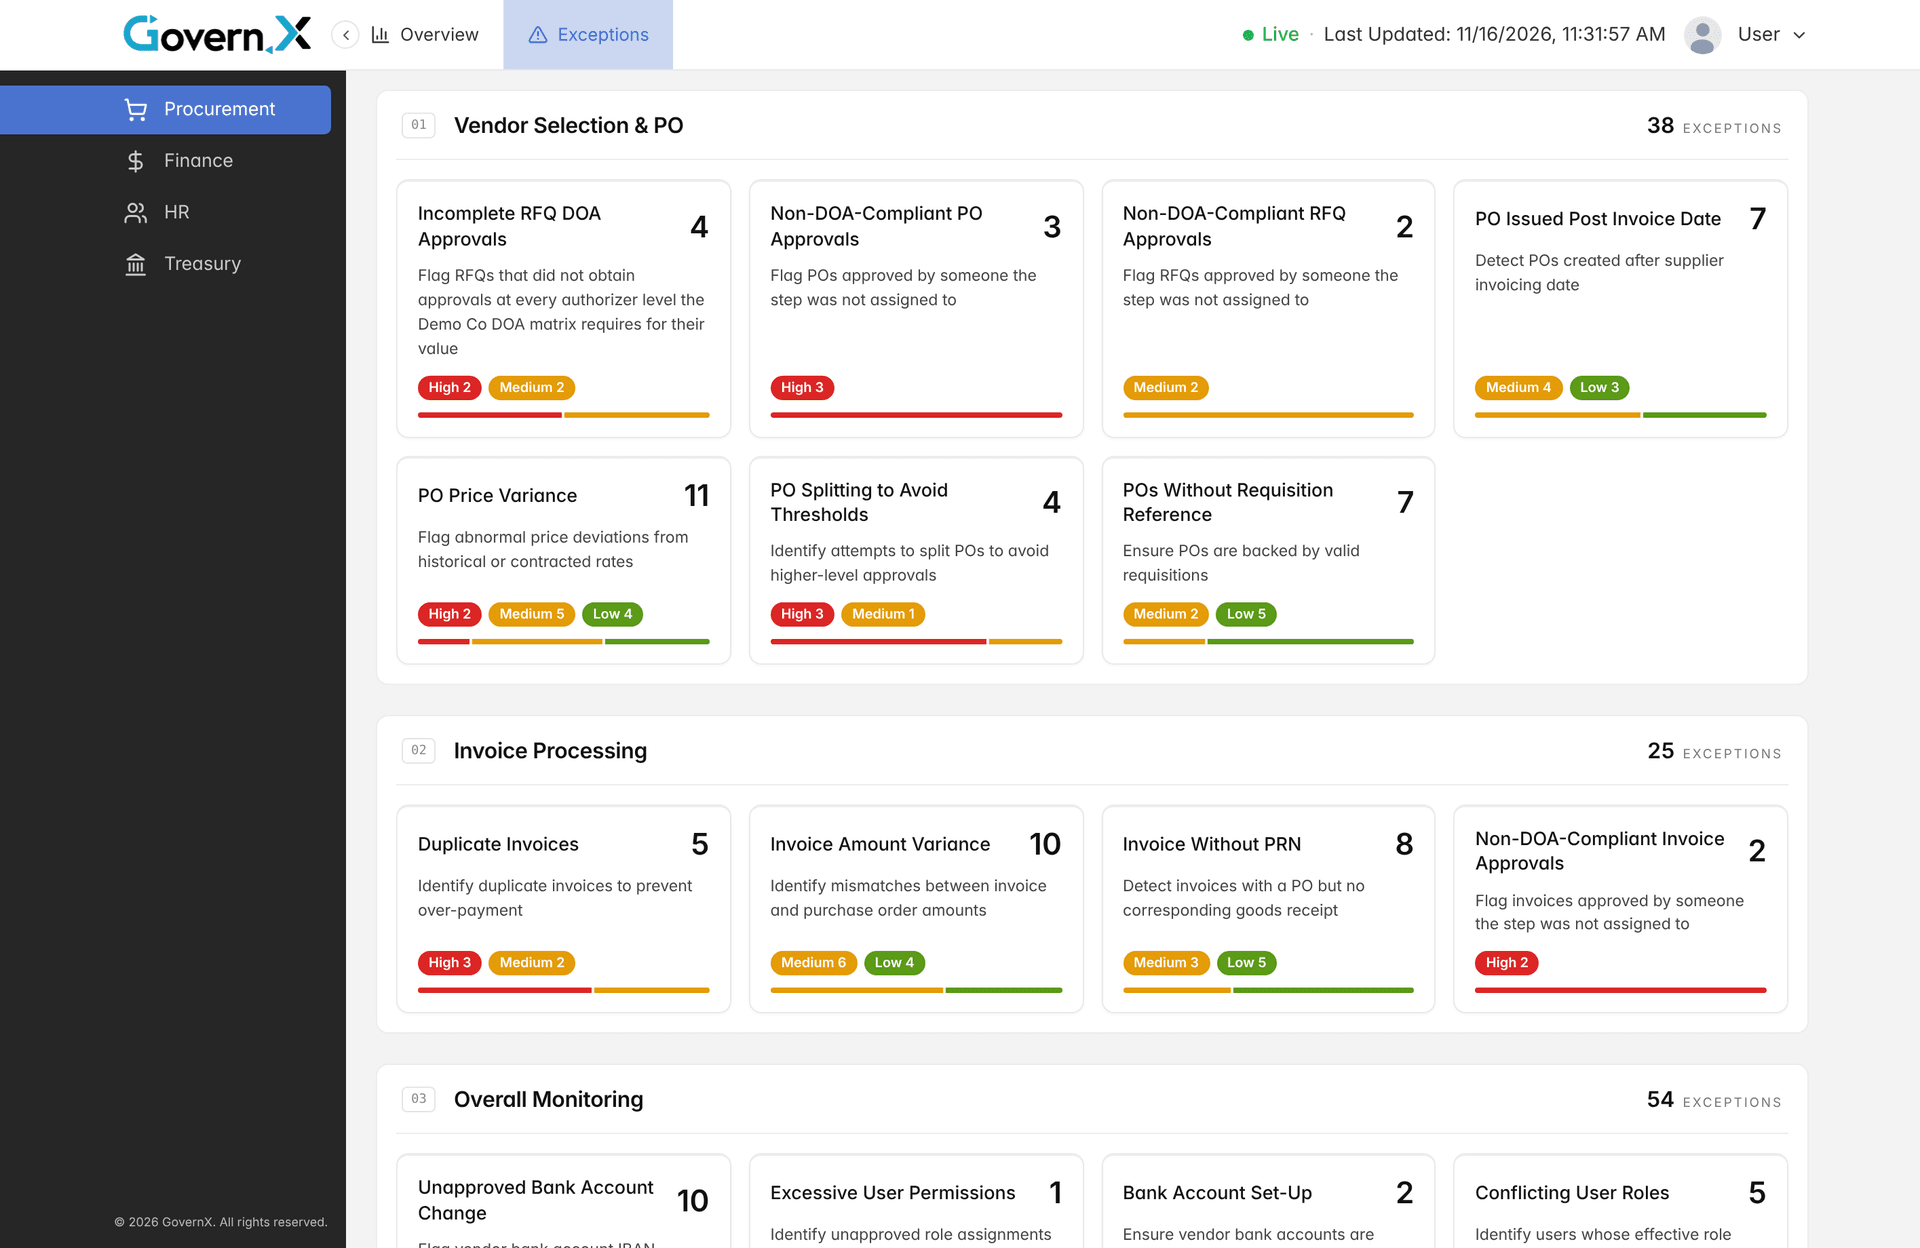
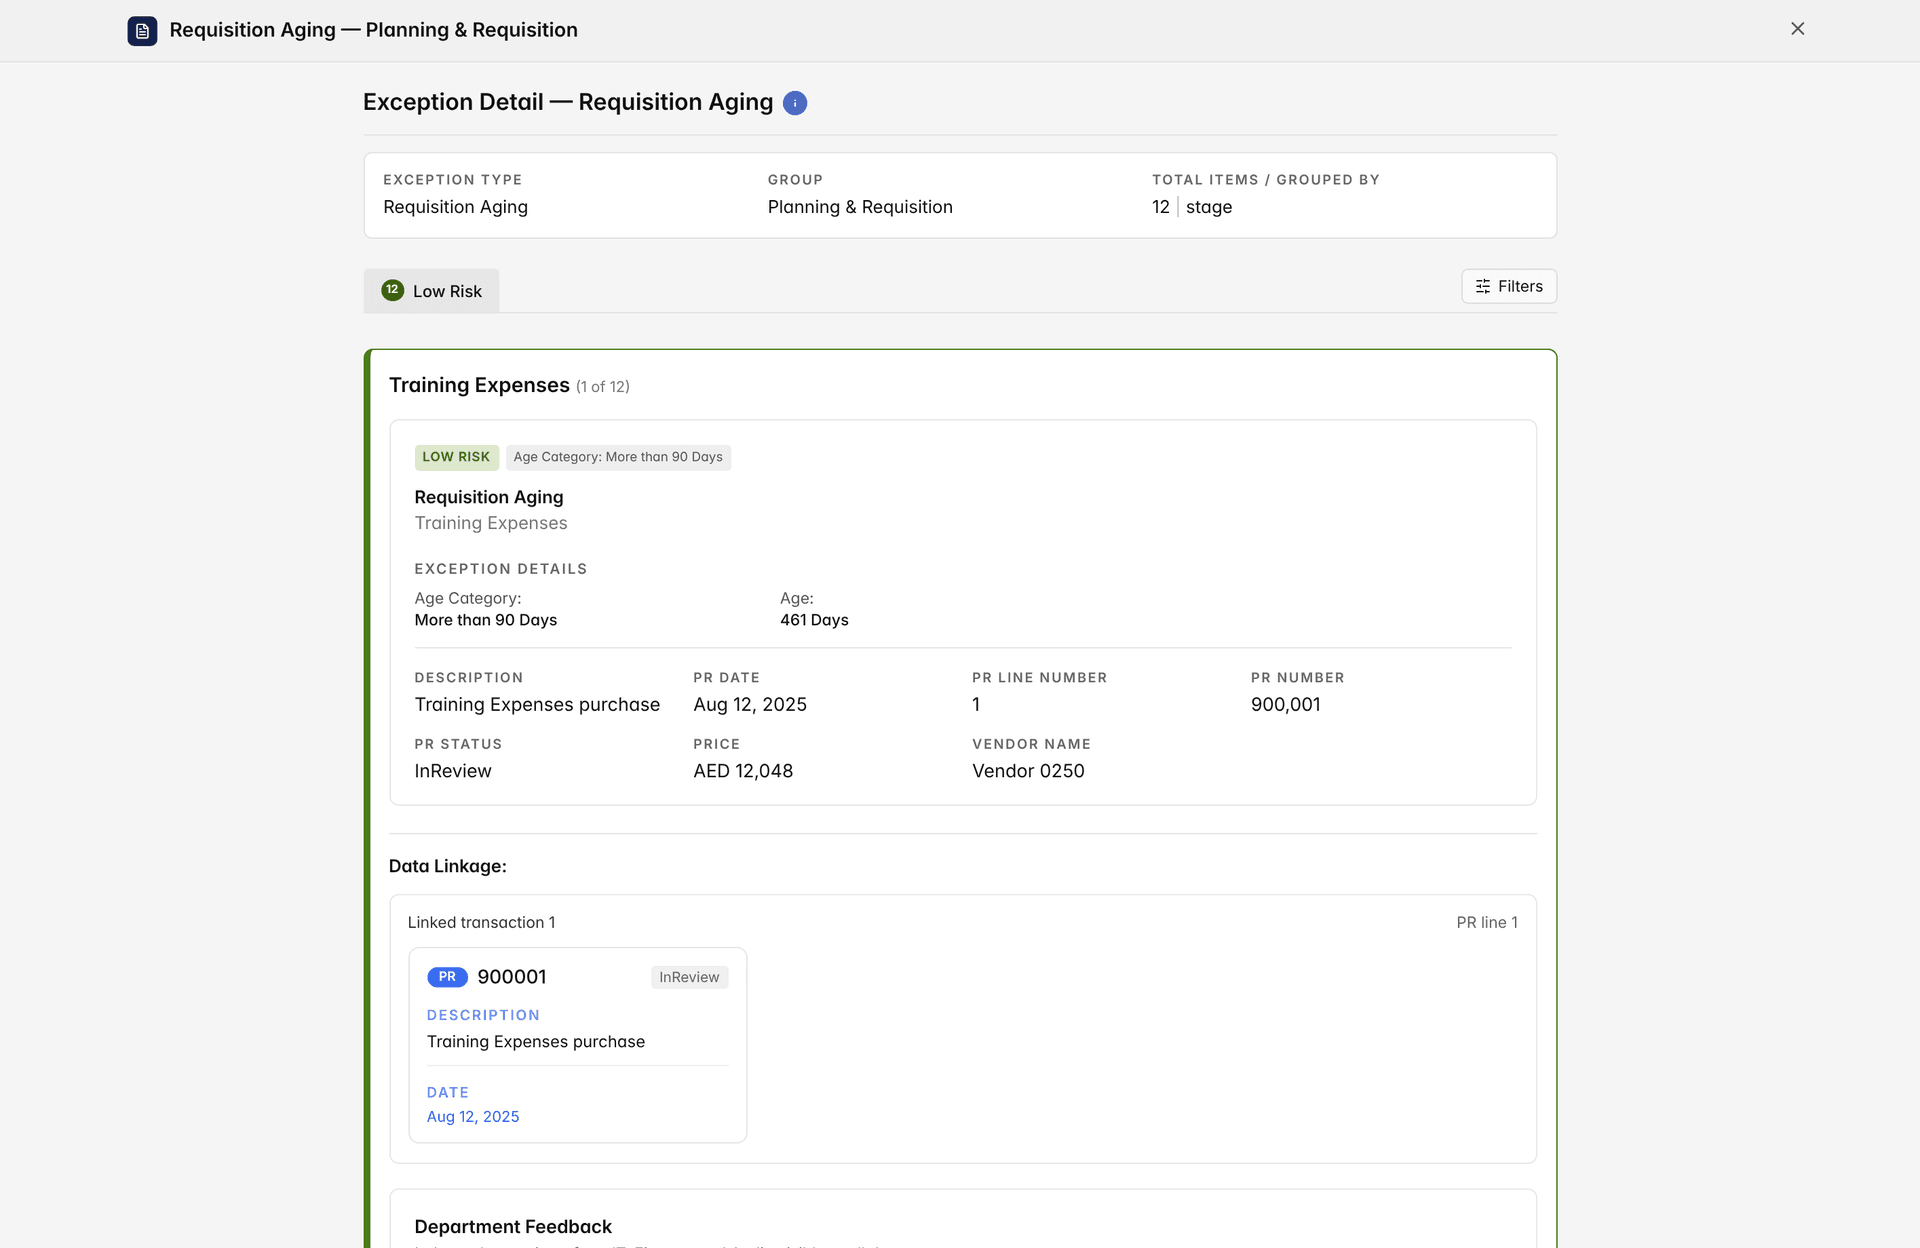
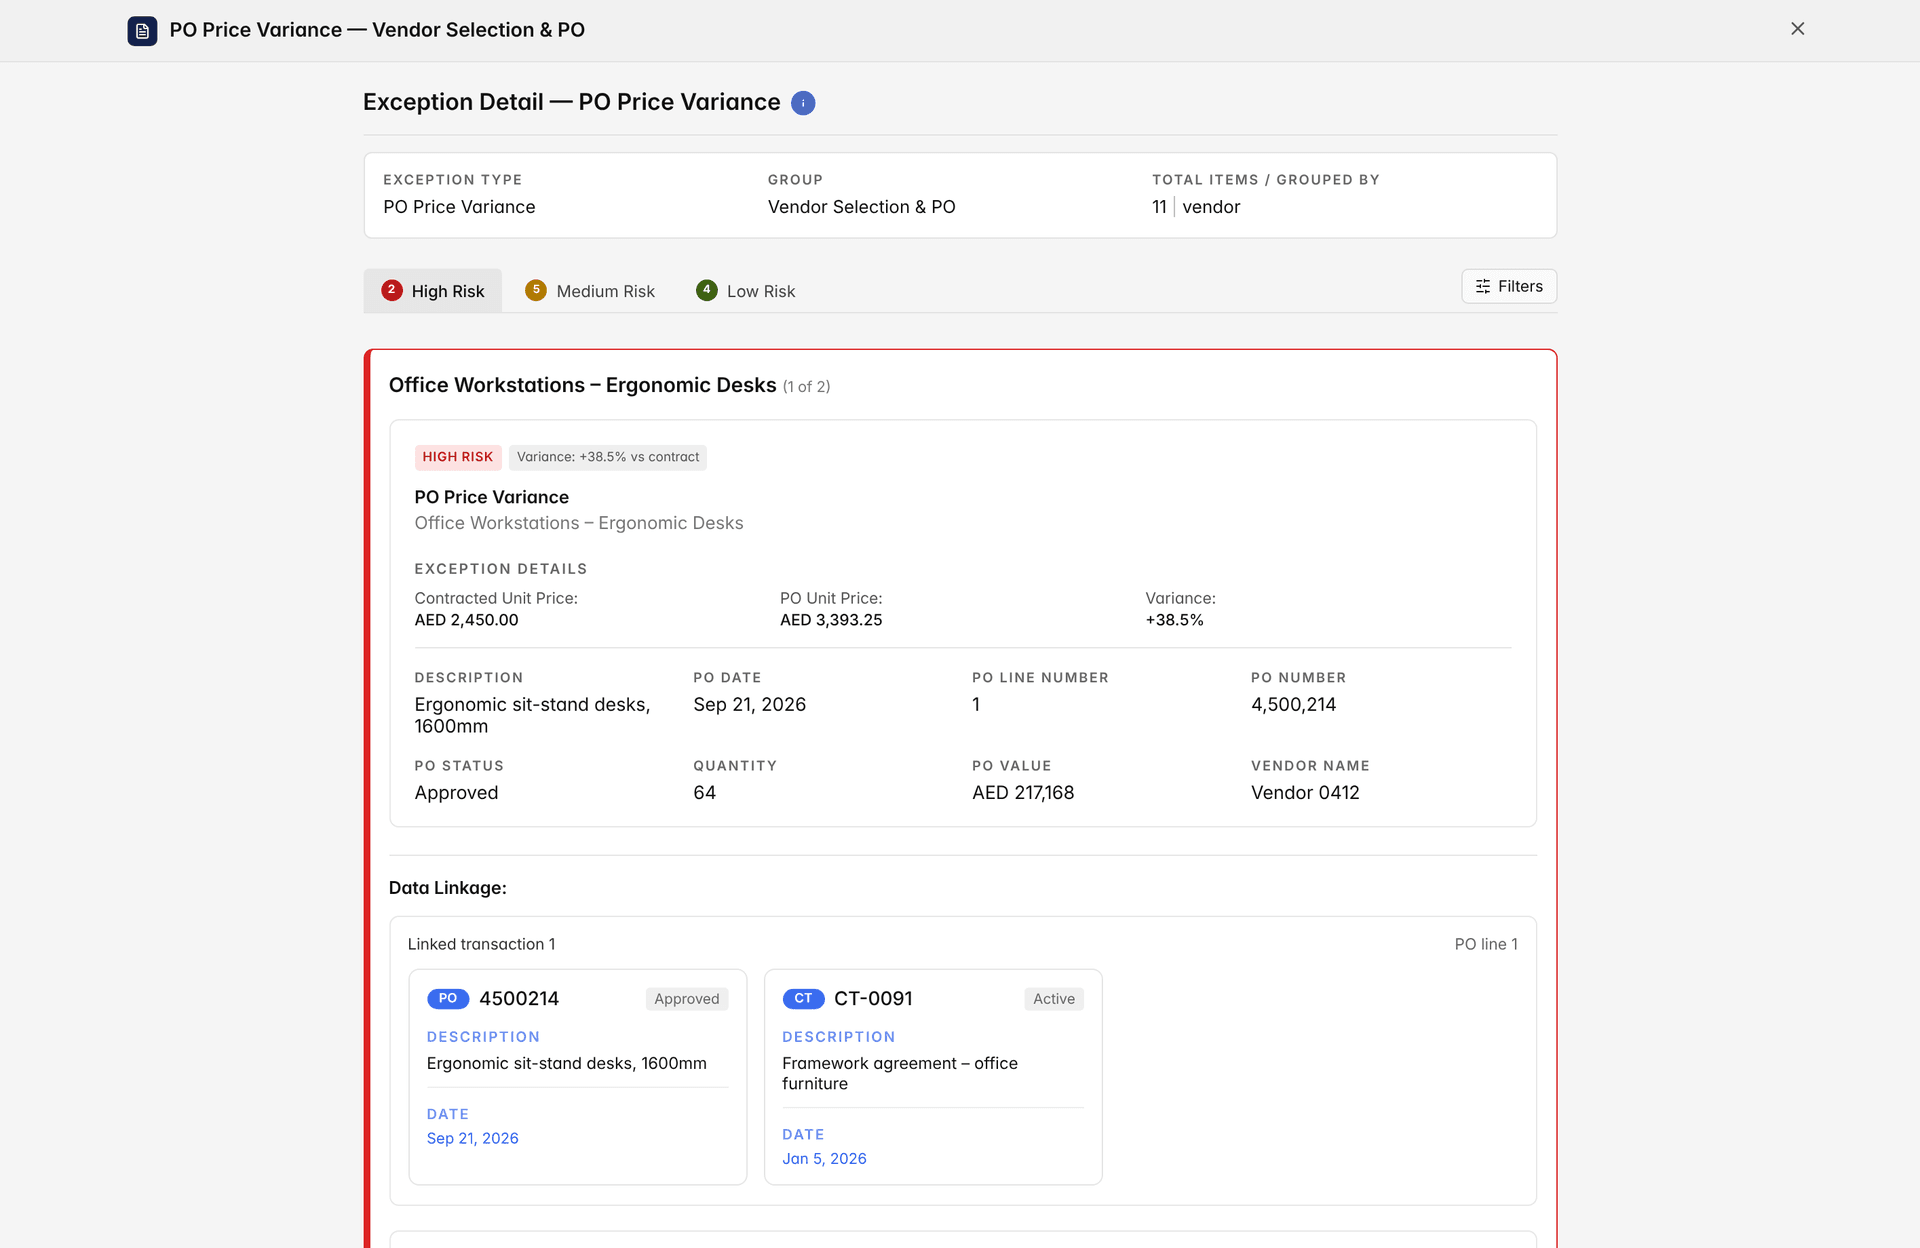
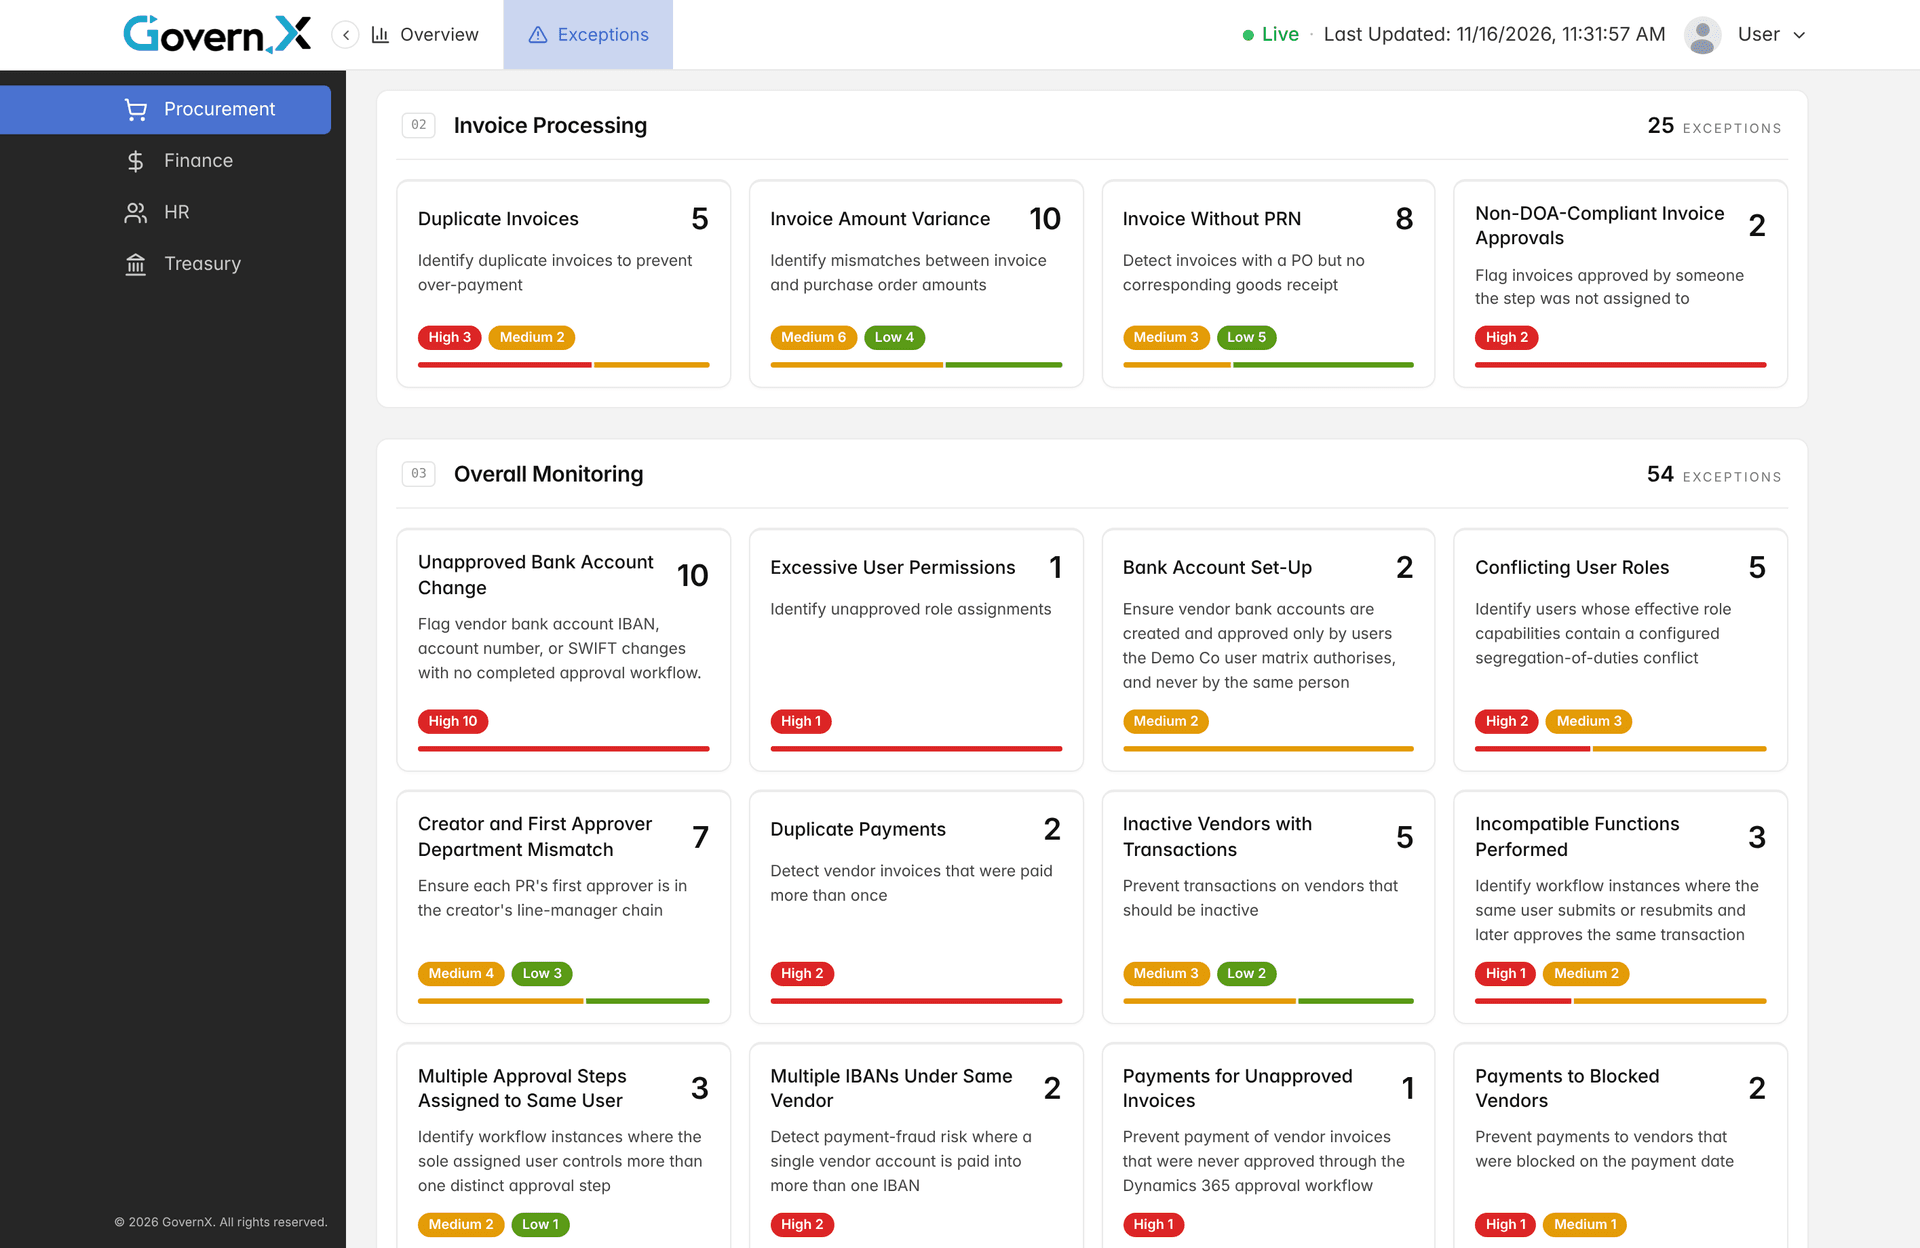
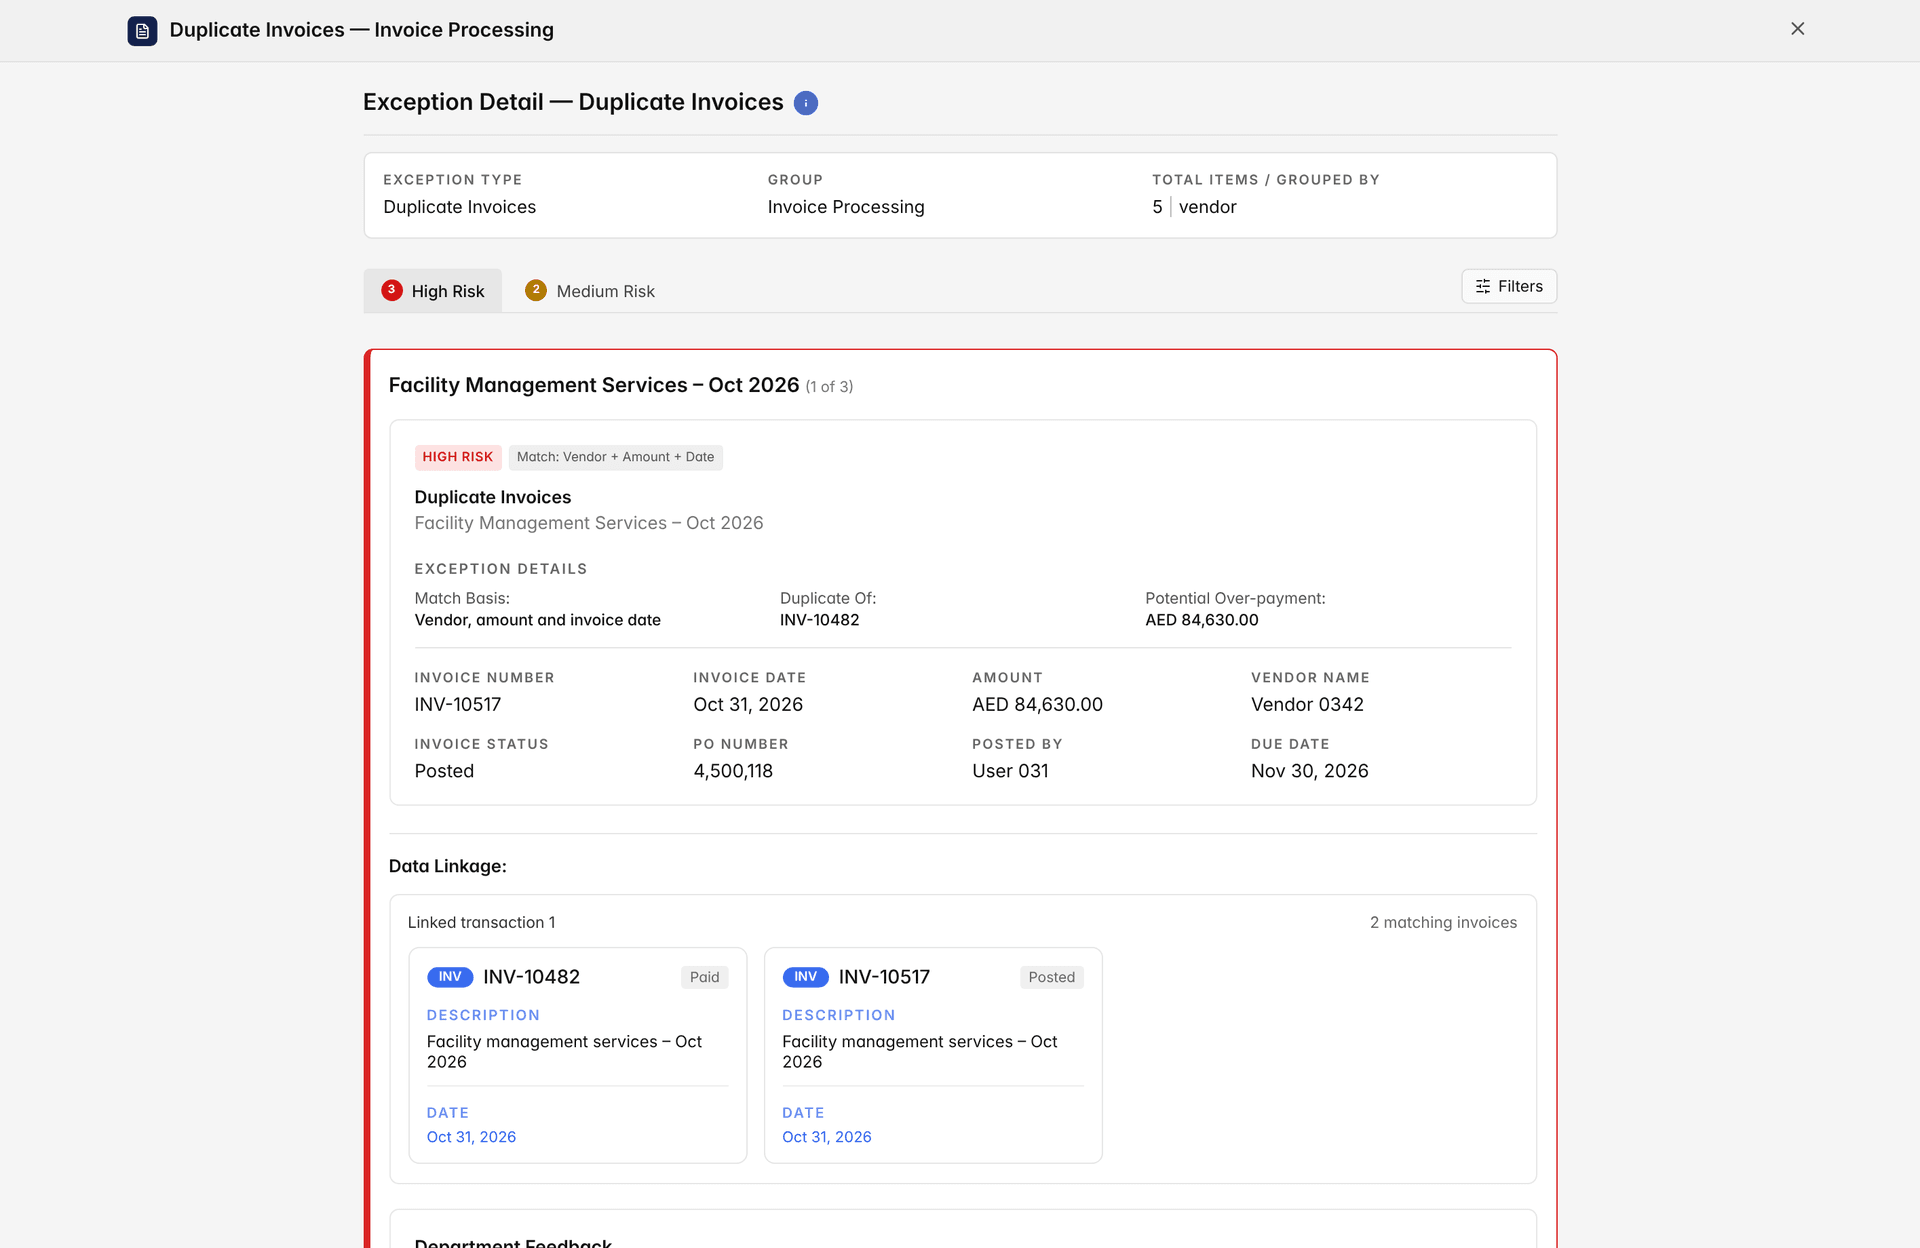
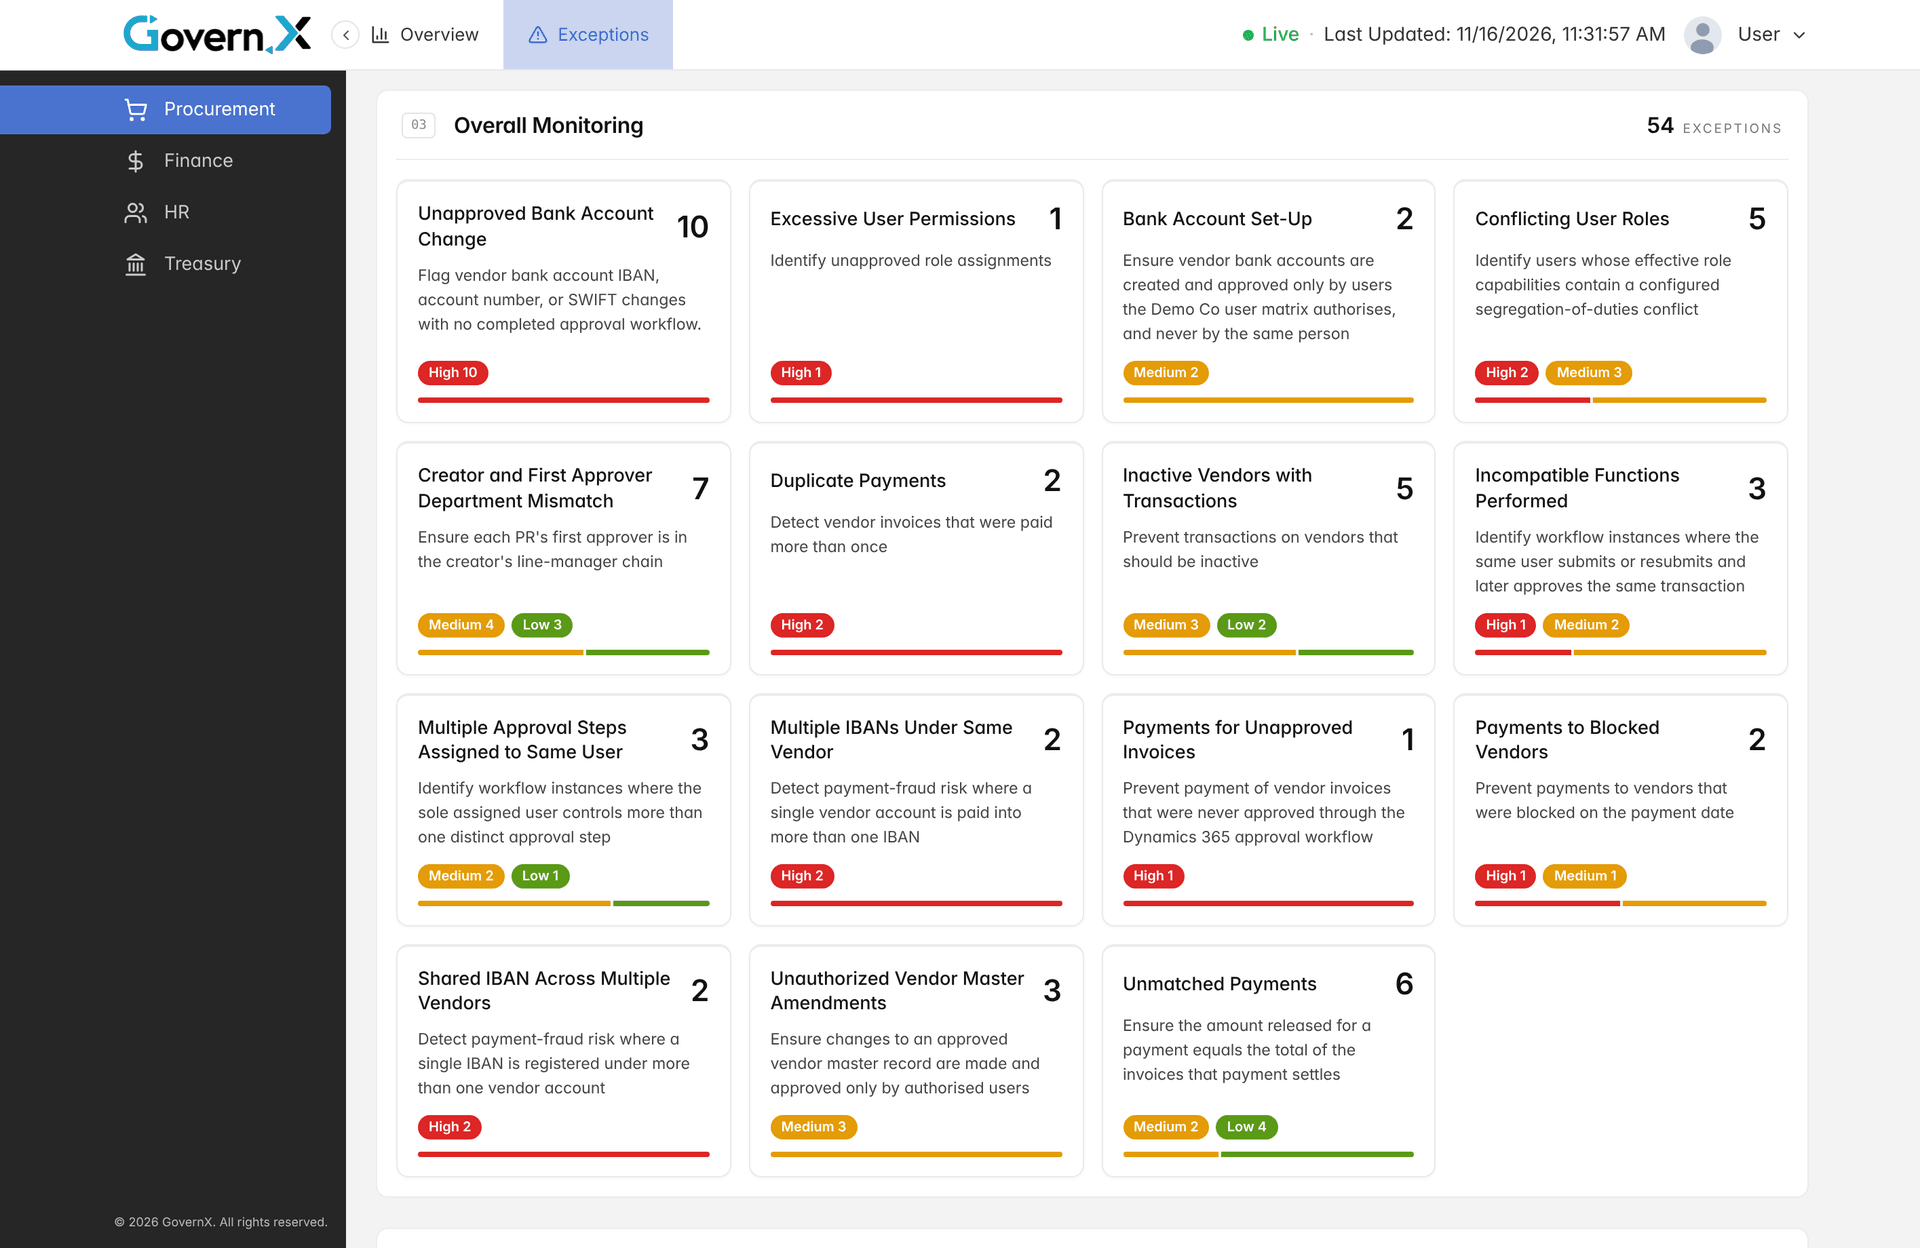
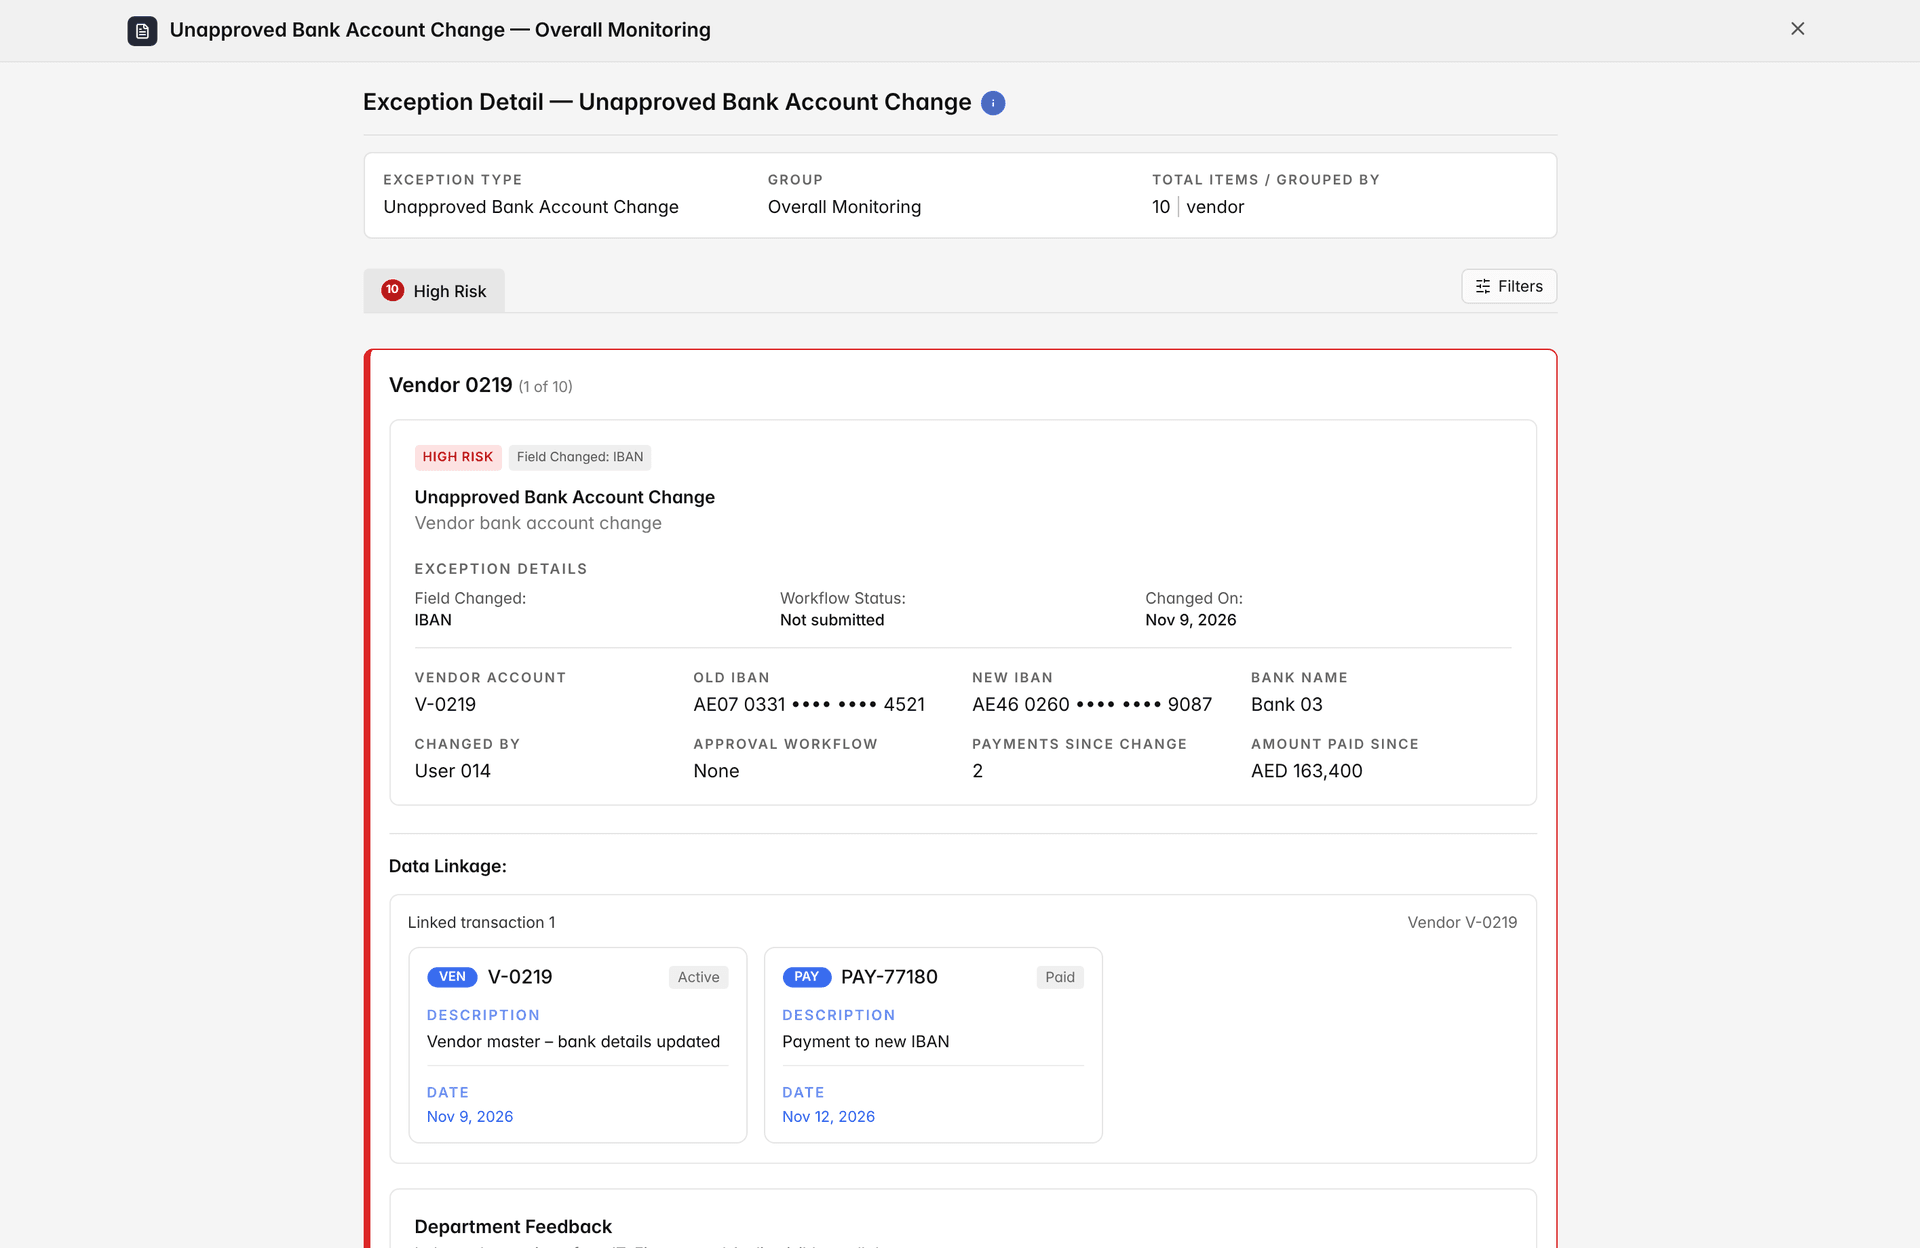
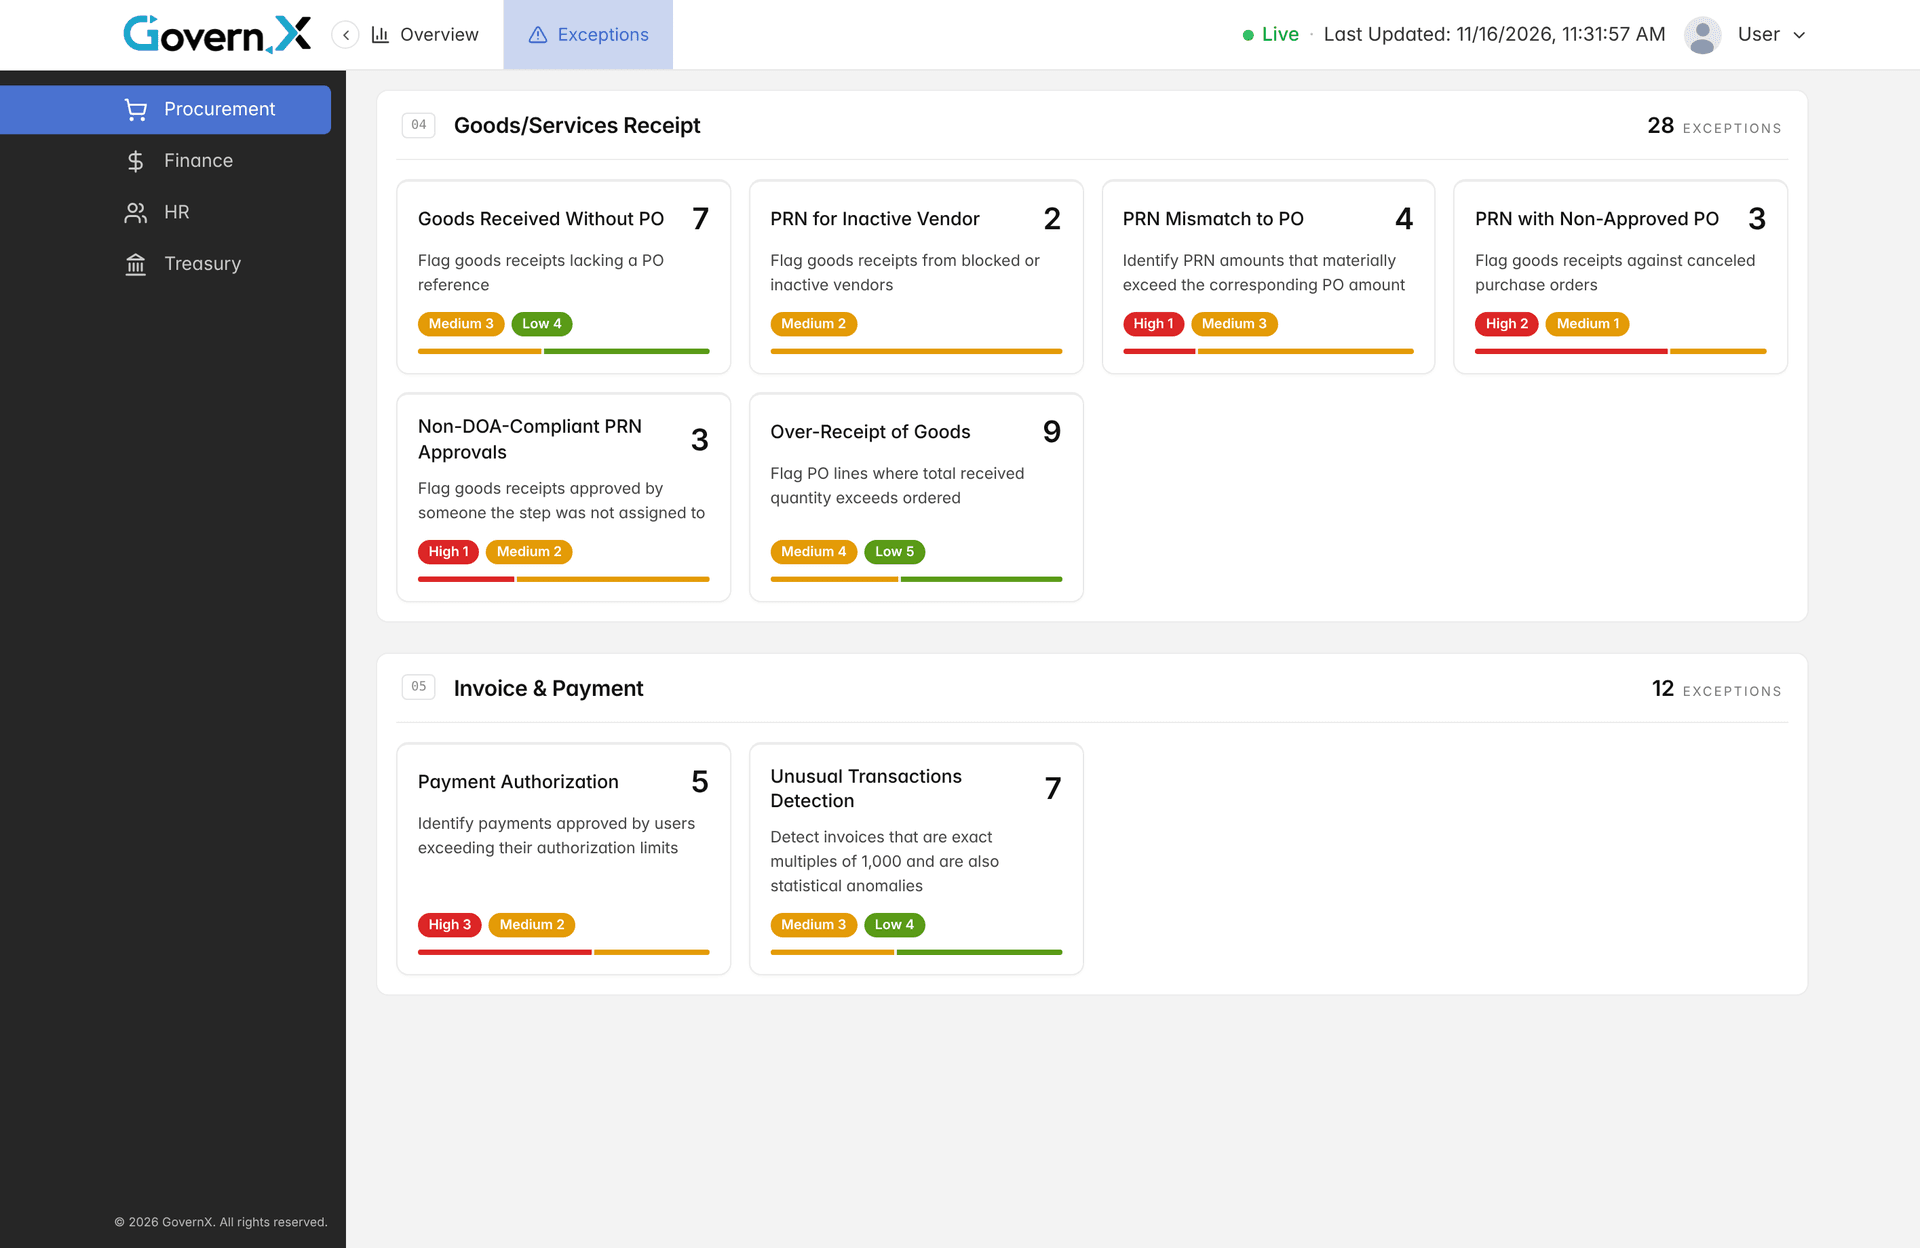
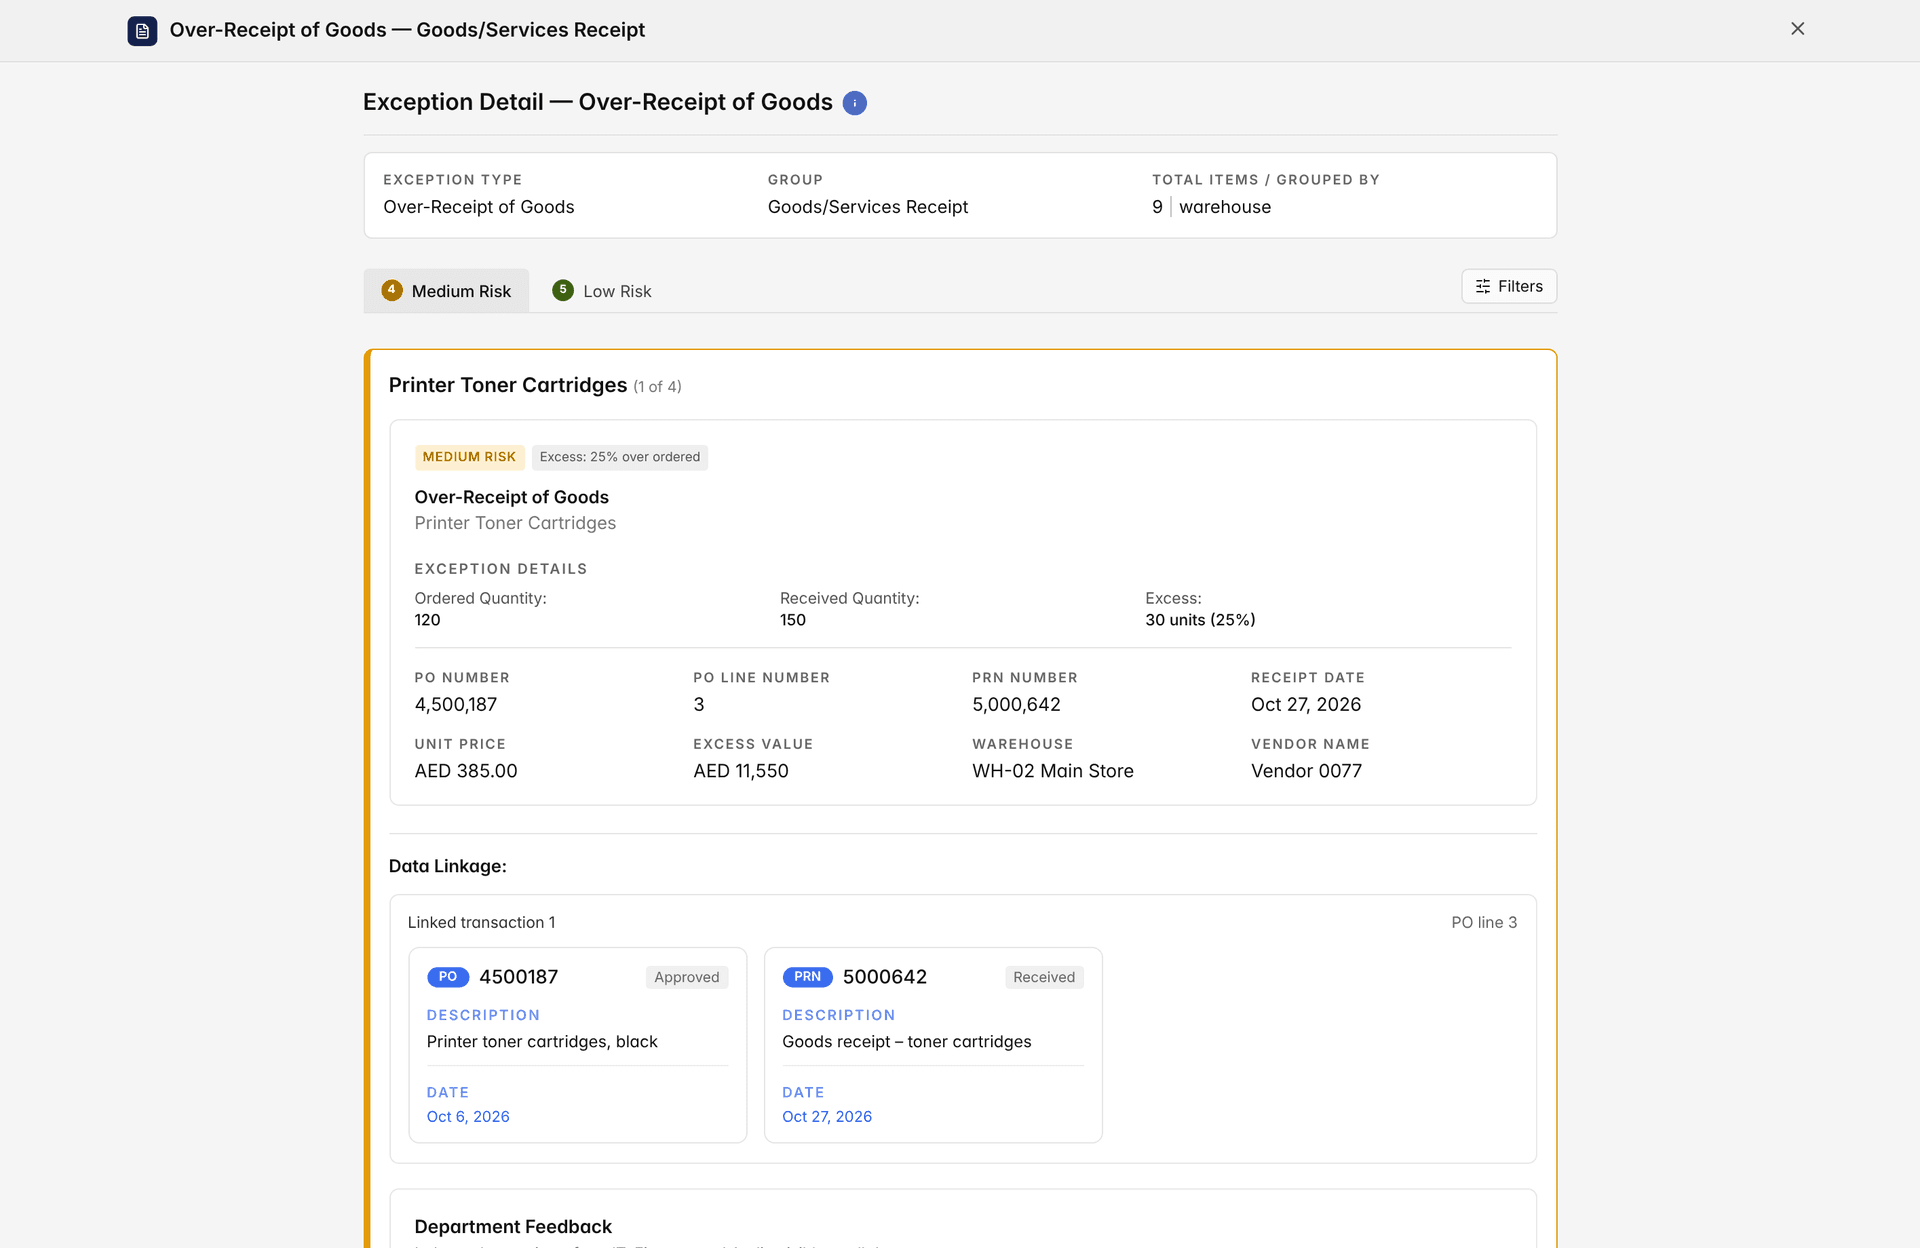
How does GovernX take you from policy to prevention?
Connect
Connect Enterprise Data sources to bring operational data into one continuously refreshed monitoring layer.
Structure
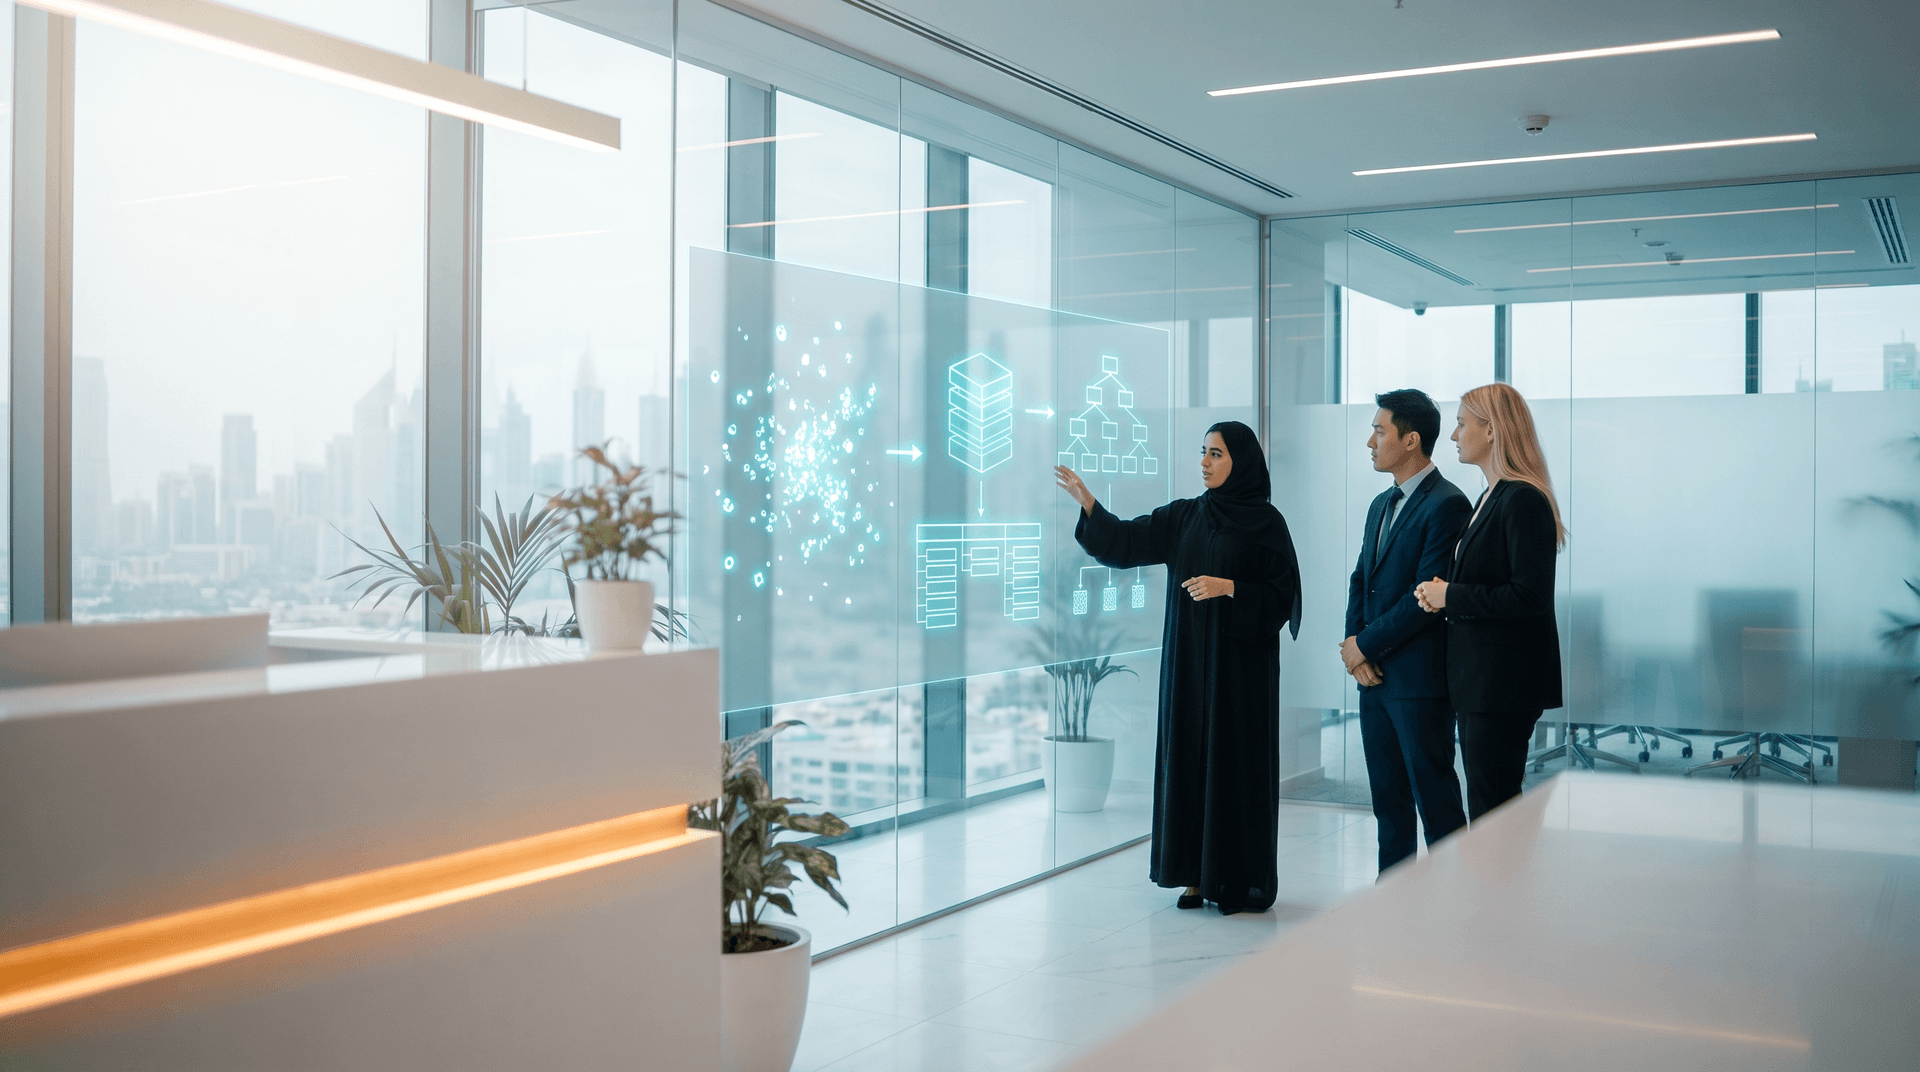
Convert policy documents into structured, machine-readable obligations mapped to the risks and controls they address.
Contextualize
Build a connected view of entities, systems, processes and controls to surface relationships and cascading risk.
Continuously monitor and detect
Test in-scope transactions continuously and surface anomalies and control failures with supporting evidence.
Why Organizations Choose GovernX
Continuous monitoring that turns organizational policies into actionable, traceable risk oversight.
100% Transaction Coverage
Test in-scope transactions continuously rather than relying on periodic audit samples.
AI-powered Policy Ingestion
Read policy documents and convert them into structured, machine-readable obligations.
Audit Universe Knowledge Graph
Model entities, systems, processes and controls as a connected risk universe.
Real-time Risk Detection
Flag policy violations, anomalies and fraud patterns as they occur.
Policy-Derived Controls
Generate tests from the organization's own policies and procedures.
Enterprise System Integration
Connect to existing ERP, databases and data platforms without replacing them.
Immutable Audit Trail
Capture data lineage and supporting evidence for audit and investigation.
Always-Current Compliance View
Maintain a current view of the control environment without manual reconciliation.